GDPR Compliance Checklist for SMBs in 2026
Data privacy regulations have become a global standard for doing business.
Even U.S.-based SMBs are now affected if they handle data from EU customers.
The General Data Protection Regulation (GDPR) sets strict rules for how personal data must be collected, stored, and processed.
Non-compliance can lead to severe financial penalties and reputational damage.
For growing businesses, GDPR readiness is now part of basic cybersecurity hygiene.
Quick Answer: GDPR Compliance Checklist
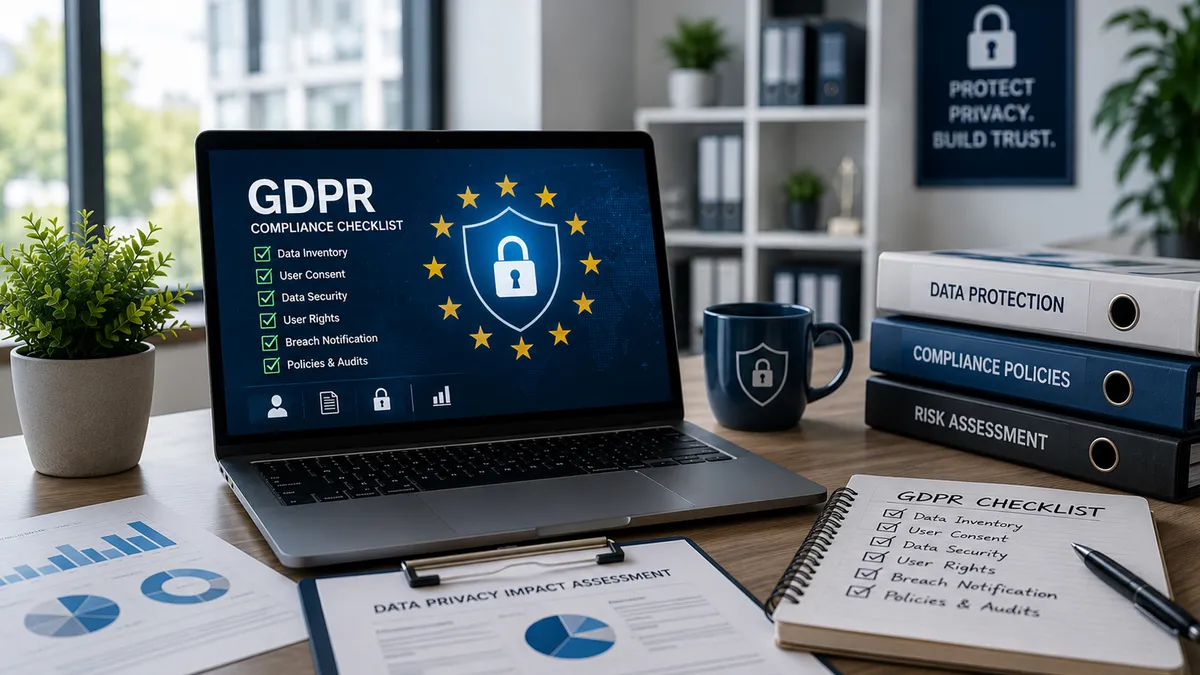
Identify and document all personal data you collect
Obtain clear consent from users before data processing
Secure data using encryption and access controls
Enable data subject rights like deletion and access requests
Maintain breach notification procedures
Regularly audit and update compliance policies
Why GDPR Matters in 2026
GDPR enforcement has become stricter and more consistent globally.
Even companies outside Europe are impacted if they serve EU customers.
Key drivers include:
Increased global data privacy expectations
Cross-border data processing requirements
Rising cyber threats targeting personal data
For SMBs, GDPR compliance helps:
Build customer trust
Avoid legal penalties
Improve overall cybersecurity posture
Key GDPR Compliance Requirements
Data Collection Transparency
Businesses must clearly explain what data is collected and why.
User Consent
Consent must be explicit, informed, and easily revocable.
Data Minimization
Only collect data that is necessary for business operations.
Storage Protection
Personal data must be encrypted and securely stored.
Risks of Non-Compliance
Fines up to millions of euros
Legal action from regulators
Loss of customer trust
Data breach exposure
How KBytes Supports GDPR Compliance
KBytes helps SMBs implement structured compliance frameworks that align with GDPR requirements.
Services Include
Data protection assessments
Security policy implementation
Endpoint and network security controls
Continuous monitoring and reporting
Learn more about managed IT services for compliance support.
Explore cybersecurity solutions designed to protect sensitive data.
Tools and Best Practices
Tools
Data encryption platforms
Access control systems
Backup and recovery tools
Monitoring and logging systems
Best Practices
Limit access to personal data
Regularly review data storage practices
Train employees on data handling
Implement incident response plans
Cost of Ignoring GDPR
Regulatory penalties
Customer churn
Brand reputation damage
Operational disruption
Step-by-Step GDPR Framework
Step 1: Assessment
Identify all data collection points.
Step 2: Risk Identification
Evaluate vulnerabilities in data storage and processing.
Step 3: Implementation
Apply encryption, policies, and consent systems.
Step 4: Monitoring
Track data access and compliance continuously.
Step 5: Improvement
Update policies as regulations evolve.
Why SMBs Choose KBytes for GDPR Compliance
Expertise in global compliance frameworks
End-to-end security implementation
Continuous monitoring and support
Scalable compliance solutions
Visit the homepage to explore compliance-ready IT services.
Real-World Use Cases
SaaS companies manage user data across regions.
E-commerce businesses process international customer data.
Financial firms handle sensitive personal information.
Healthcare platforms secure patient-related data.
Marketing agencies manage customer databases.
FAQs
Conclusion
GDPR compliance is essential for any business handling personal data.
It improves trust, security, and legal protection.
Partner with KBytes to build a compliant and secure IT environment.
Request a consultation or compliance assessment today.

